Why a new discipline, and why now.
Software changes between security engagements, and since 2026 frontier models have found and exploited the gaps in hours. A finding needs an owner, a verified fix and a check that catches the same failure again, or it stays a report.
We started with measurement. SecLens, our benchmark, scored frontier models on real vulnerabilities and found two things a buyer should know: the same model rates very differently depending on who is asking, and every model misses whole classes of vulnerability. A security programme built on one model’s score inherits that model’s blind spots.
That research, and securing the first organisations against exploits of this new kind, convinced us the work needed one loop and one name. ExploitOps is the practice Mattersec Labs introduced in 2026: observe what changes, prove what is exploitable, fix it with the team that owns the code, remember the fix as a check. MATT is the product that runs it.
Read SecLens ↗SecLens on GitHub ↗The MatterSec 50 ↗Research at mattersec.com ↗
The two people behind it.
-
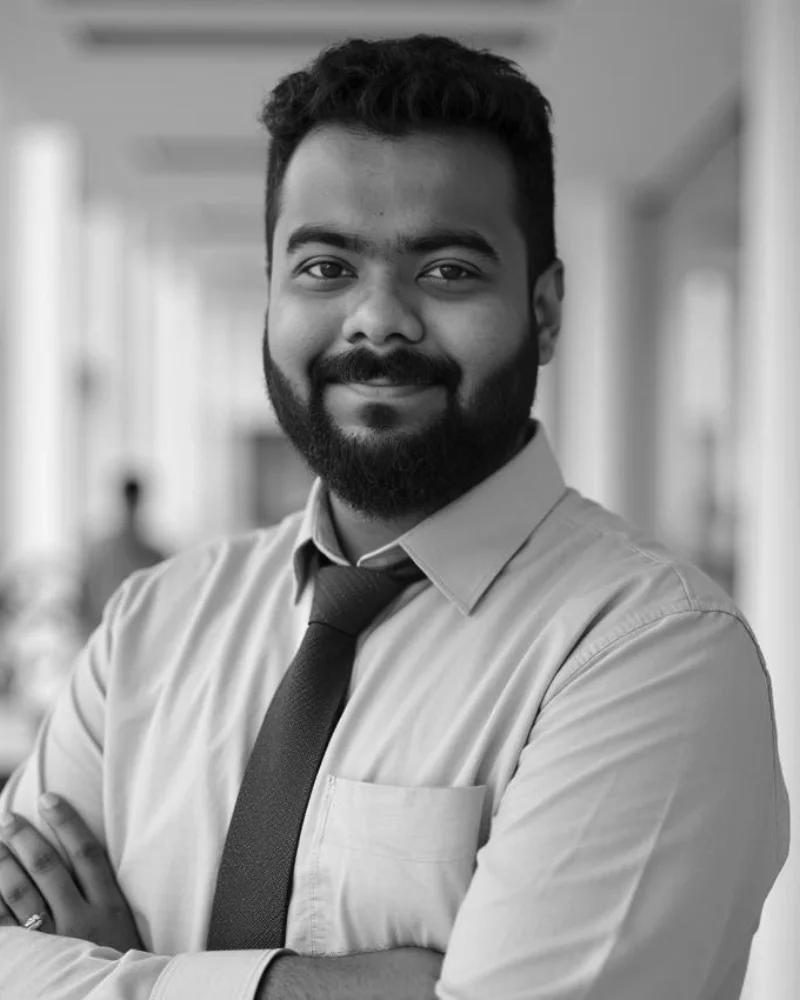
Subho Halder
Co-founder & CEOCo-founded Appknox in 2014 and led it for twelve years, first as CTO and then as CEO, building mobile application security for enterprises. Lead author of SecLens, the benchmark of how frontier models detect security vulnerabilities. In application security since 2012, with acknowledgements from Apple, Google, Facebook and Microsoft. At Mattersec Labs, Subho leads MATT: the product, the research and the engagements.
-
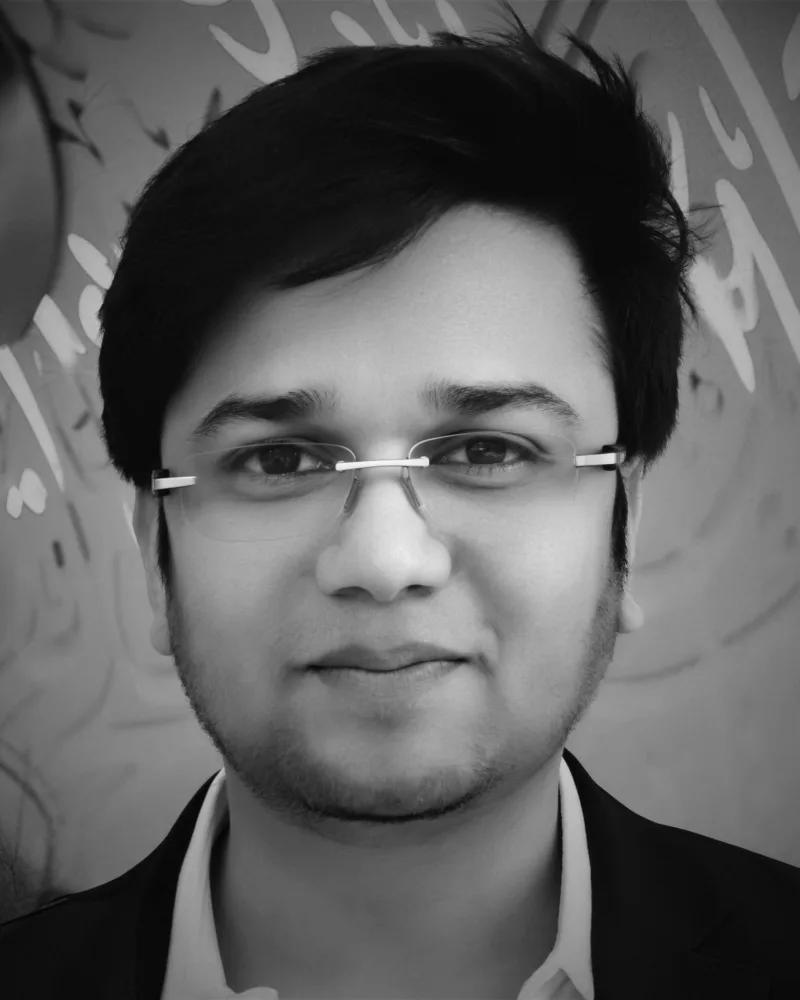
Aishwarya Jain
Co-founder & CBORuns the commercial side of Mattersec Labs: customers, partnerships and go-to-market. Most of AJ’s work has been in crypto and blockchain: token launches, go-to-market and ecosystem growth for Web3 projects from Dubai, and advising CredShields, the Web3 security auditor, on security. The lesson of those years, that speed without trust creates risk, is why Mattersec exists.
Six things you can hold us to.
- 01
Proof, before anything else.
A finding is a working attack path in the agreed test environment, with the request and the response attached. Where a path cannot be reproduced safely, we say so and record it as a risk with the evidence we have.
- 02
Your engineers approve every change.
Fixes are written with the team that owns the code and merged by them. The first engagement is manual by design, so the rules are understood before anything runs on its own.
- 03
Rules a board can read.
Each fix becomes a plain-English rule. Where a check can run automatically it does, on every release; where it needs a person, the rule says who and when.
- 04
We say exactly what we touched.
The audit works from read access to your repository and a test login in an agreed test environment; the engagement letter sets the scope, permissions and handling before we start. Production data, secrets and customer records stay out of scope, and the final report lists every system actually assessed.
- 05
Your pentest still counts.
Penetration tests, AppSec programmes and bug bounties feed the loop. ExploitOps carries their findings through the fix, the verification and the check that catches the regression.
- 06
Incidents, in the companies’ own words.
The Record quotes official disclosures, dates and numbers, with one neutral pattern line. What we would have caught in someone else’s breach stays unsaid.
Proof, with links.
Selected public research, acknowledgements and conference records, each linked to its source.
The full list of talks, trainings and Arsenal demos since 2012 is on subhohalder.com.
- Apple security notes ↗ iOS 7 security acknowledgement, CVE-2013-0926
- Meta leaderboard ↗ Bug bounty leaderboard
- The Verge ↗ Press coverage
- Black Hat ↗ Trainer, Mobile Hacking Summit, Black Hat USA
- Black Hat ↗ Arsenal, Devknox, Black Hat USA and Asia
- Black Hat ↗ Speaker, Black Hat Abu Dhabi
- OWASP Foundation ↗ Speaker, mobile kernel code and RASP evasion
- MSRC archive ↗ MSRC acknowledgement
The company, in seven lines.
- Company
- Mattersec Labs Inc., a Delaware corporation
- Where we work
- San Francisco, Dubai and Bangalore
- What we make
- MATT, the AI Security Supervisor for the modern software lifecycle
- How it runs
- ExploitOps: observe, prove, fix, remember
- How it starts
- A sixty-minute ExploitOps Review to agree fit and priorities, then a scoped audit, then MATT on your release cycle
- Appknox
- Distribution partner for MATT; the mobile application security company Subho co-founded and led
- Research
- SecLens and the MatterSec 50, published by Mattersec Labs
- Write to us
- contact@matt.security